Organizational Support in AgentZ
AgentZ gives a company an organization, a workspace for each team, roles, and shared resources that an admin sets up once.
Sign-Up Creates an Organization
You cannot create an organization by hand. When a user signs up, AgentZ creates one and makes that user the Superadmin, the built-in role with every capability. A user can belong to several organizations and switch between them from the account menu.
Only a Superadmin creates workspaces. A workspace is the home of one team. Its agents, secrets, workflows, triggers and dashboards live there.
graph TD
    ORG["Organization"] --> WS["Workspace per team"]
    WS --> AG["Agents, secrets, workflows,<br/>triggers, dashboards"]
    ORG --> RES["Shared once: skills, sandboxes,<br/>MCP connections,<br/>inference providers"]
    RES -. "inherited when selected" .-> WS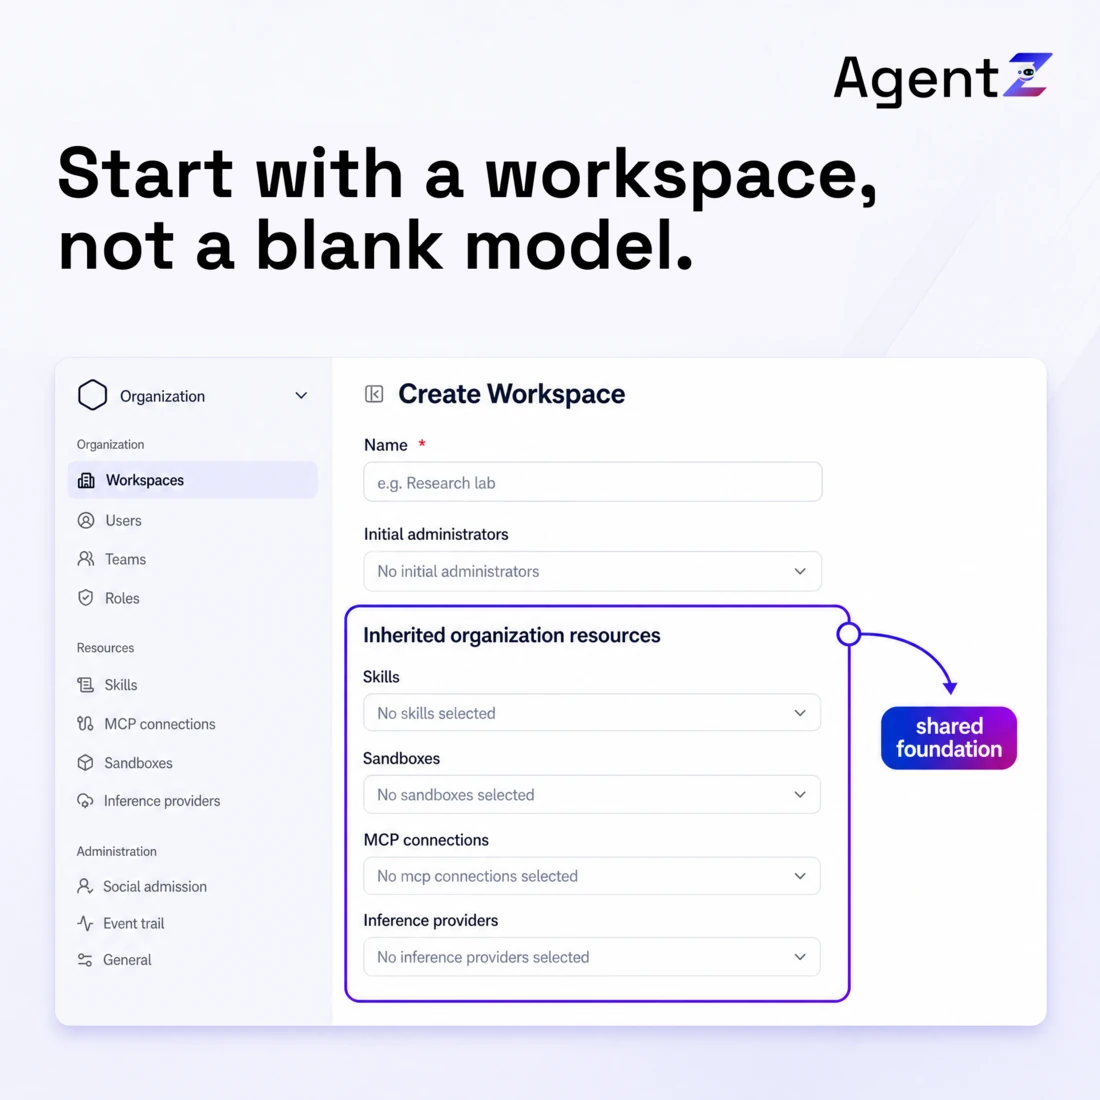
Admins Set Shared Resources Once
An admin adds skills, sandboxes, MCP connections and inference providers at the organization level. A workspace inherits the ones you select when you create it. The inherited resources are read-only inside the workspace.
AgentZ does not add resources created later. You select them for each workspace. AgentZ also blocks a removal while something uses the resource. For example, you cannot delete an MCP connection that a sandbox references.
Roles Decide Who Can Do What
A role is a named set of permissions. Attach it to a person or to a team. AgentZ ships two built-in roles, Superadmin and Workspace Admin. You build every other role.
Access to a resource has up to four levels: read-only, read and create, read, create and modify, and full access. A role can hold different grants for the organization and for each workspace. A user with no role and no team has no access.
You Can Share Only What the Target Already Holds
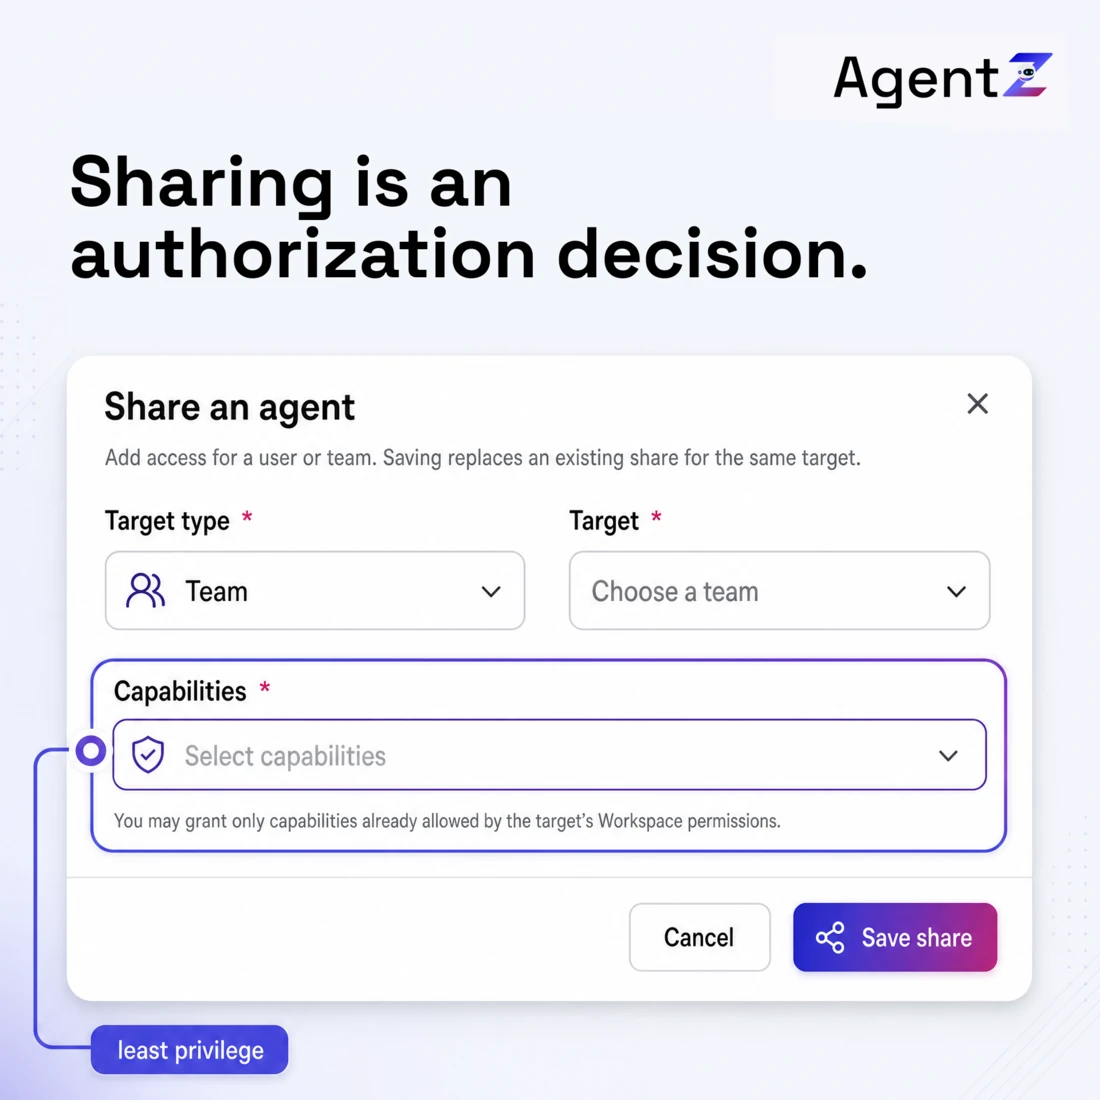
The creator of an agent can use, change and delete it. To let others use it, you share it with a user or a team. You can grant only capabilities that the target already holds in that workspace.
Social Sign-Up Sets Default Access
An admin creates an invitation link that carries at least one role or team. The link works once and expires after 48 hours. With Social admission, people join through Google or GitHub. Rules for Google email domains and GitHub organizations decide who may join. Default roles and teams decide what they get.
The Event Trail Records Admin Changes
The Event trail shows who changed what, and when. Each entry names the actor, the action, the target and the result. AgentZ keeps entries for 30 days.
Next Step
Set up access with Roles and teams.